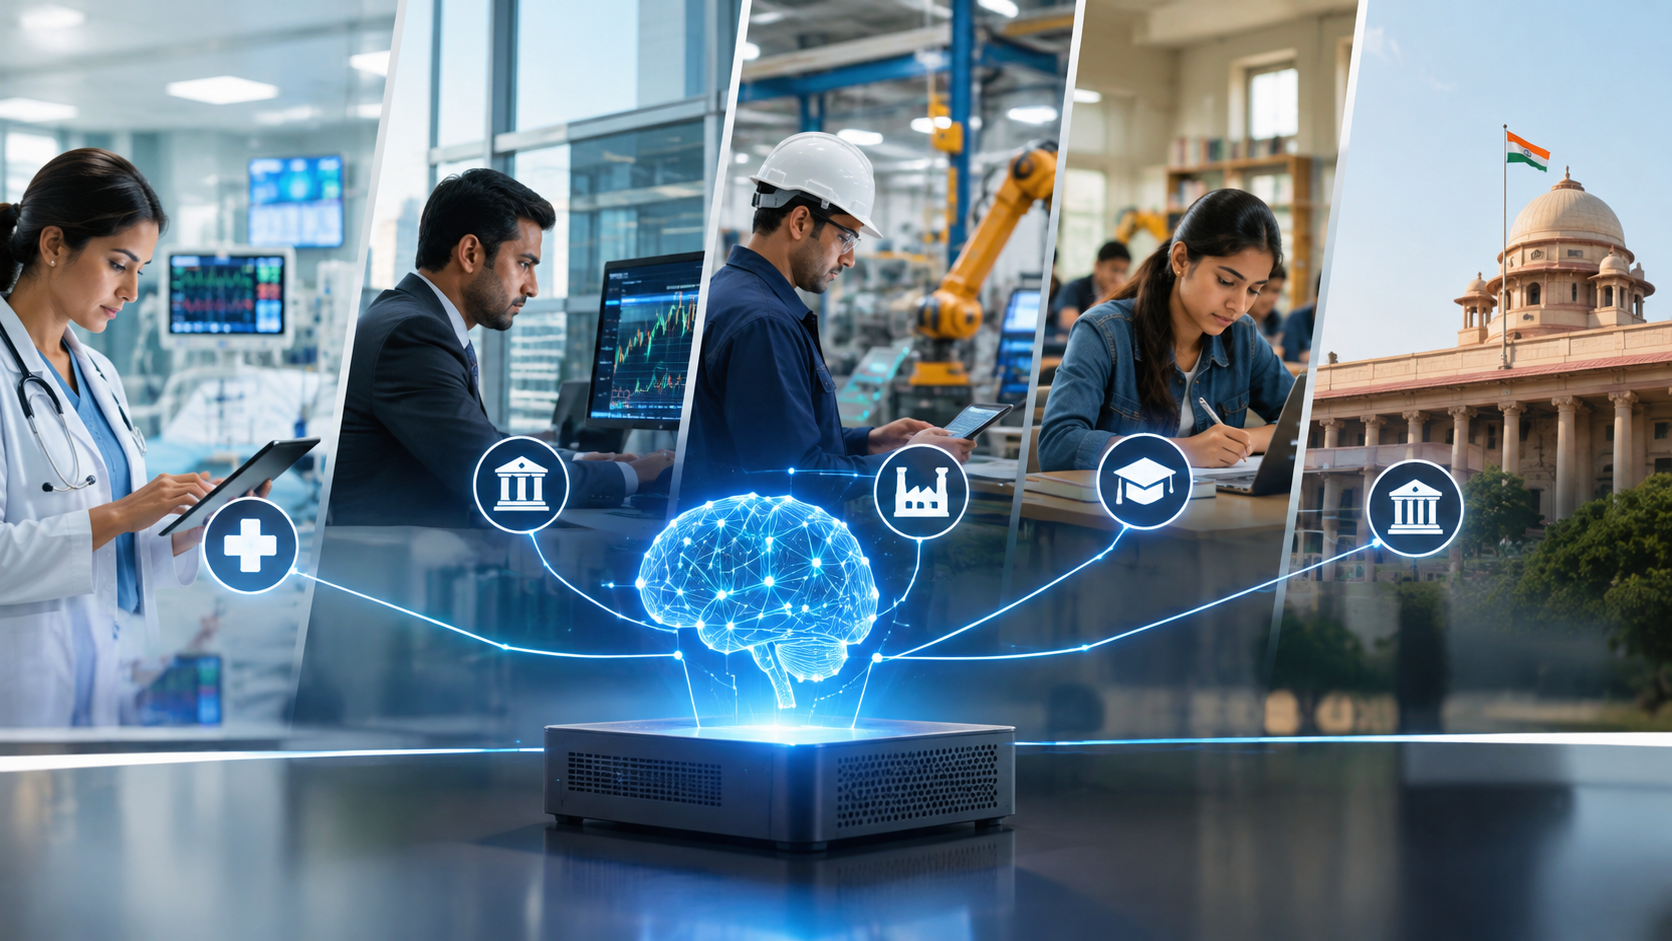
"Regulated" is not one condition. A hospital, a bank, a ministry and a manufacturer face constraints that differ in source, in force and in what they demand of an architecture — and a programme designed against a generic notion of compliance will over-build in one place and under-build in another.
This is the sector-by-sector version of the AI transformation path. Every instrument cited here is named with its status, because the fastest way to lose a regulated buyer is to cite a regulation incorrectly to the person in the room who has read it.
Healthcare
Sector detail: on-premise clinical AI for hospitals.
What governs it. The DPDP Act 2023 read with the DPDP Rules 2025, plus the ABDM Health Data Management Policy for participants in that ecosystem — a National Health Authority policy revised April 2022, which relies on the IT Act 2000 and DPDP for legal force. HIPAA applies where a US covered entity is in scope.
What does not govern it. DISHA was never enacted. Proposed in 2017, redrafted in 2022, still not law. It imposes no obligation on anyone and cannot be cited as a compliance driver.
Worth knowing for conversations with US-linked entities: HIPAA does not currently mandate encryption or MFA. Those are proposals in the NPRM published 6 January 2025, with a final rule indicated around July 2027. The current Security Rule has required and addressable specifications, a Business Associate Agreement requirement, and audit controls.
What it means architecturally. ABDM's federated model — records staying with the creating facility rather than moving to a central store — aligns naturally with on-premise retrieval, because the index sits where the records already are. The demanding requirement is permission inheritance: clinical systems have granular, role-based access, and an index that flattens it will surface a record to someone who could not open it in the source system. That failure is invisible in testing, because pilot users are typically clinicians with broad access.
Banking and financial services
Sector detail: AI for banks and NBFCs.
What governs it. Two RBI instruments, both in force, both structural.
The Storage of Payment System Data circular of 6 April 2018 requires end-to-end payment transaction data to be stored only in India — the foreign leg of a transaction may also be stored abroad. This is hard localisation, and no contractual assurance satisfies it.
The Master Direction on Outsourcing of IT Services, effective 1 October 2023, requires outsourcing agreements to address data localisation and to preserve both the regulated entity's and the RBI's access and audit rights, without impeding supervision. The consequence most institutions have not fully absorbed: a cloud AI API used on regulated data is an IT outsourcing arrangement. It is not a software purchase; it is an arrangement the direction covers.
The correction that matters here. DPDP does not impose a general data residency requirement — §16 is a restriction list, not a prohibition. Localisation for Indian financial data comes from the RBI, not from DPDP. Getting this backwards in a bank is costly, because their compliance function knows the difference.
What it means architecturally. The audit-rights requirement is the design driver. Whatever runs on regulated data has to be inspectable by the institution and, in principle, by the regulator. That favours a system whose request path is fixed and recorded — privacy filter, injection scanner, model, output validator, audit chain, no bypass — over one whose processing happens somewhere you can only describe.
Government and public sector
Sector detail: air-gap-ready AI for government and PSUs.
What governs it. DPDP for personal data, procurement rules for how the system is bought, and — for defence-adjacent work — requirements that often exceed anything in the civil regime.
What it means architecturally. Two things dominate. Air-gap readiness: the system must be able to run with no internet dependency at all, which is an architectural property rather than a firewall rule — model weights, dependencies and update paths all have to be resolvable offline. And jurisdictional evidence: procurement increasingly asks not where data is supposed to be, but where processing demonstrably happened, which is again an audit-record question.
A practical note on language: "air-gap-ready" is the accurate claim for a system designed to run disconnected. "Air-gapped" describes a specific deployment that actually is. The distinction is worth maintaining, because in this sector someone will check.
Manufacturing
Sector detail: AI on the factory floor.
What governs it. Often nothing sector-specific — and that is exactly why the exposure is misjudged.
What is at stake is process knowledge — tolerances, supplier terms and drawings.
What it means architecturally. CAD and drawing corpora stress the parsing layer hardest — drawings without a vector layer degrade parsing quality, and that should be measured per corpus rather than assumed.
Education
Sector detail: AI for universities, schools and L&D.
What governs it. DPDP for student personal data. Institutional policy for research material.
What it means architecturally. The distinguishing requirement is usually linguistic rather than regulatory — genuine multilingual operation across Indian languages as a functional requirement, not a localisation layer. Plus the ordinary but non-trivial demand that student data and institutional research not become training material for someone else's model.
What is common across all of them
Smaller organisations face the same constraints at smaller volume — see AI for SMBs.
Strip out the sector specifics and the same three requirements appear:
- Permission inheritance from source systems into the retrieval index. Every sector above has granular access control in its systems of record, and every one of them breaks if the index flattens it.
- A per-decision audit record covering retrieved context, not just requests — tamper-evident, retained. DPDP Rule 6 asks for a year of access logs with breach reporting at 72 hours and no materiality threshold, and RBI asks for audit rights. Both are satisfied by the same record.
- A failure mode of refusal. In a fail-closed on-premise mode, a misconfiguration stops the request rather than silently transmitting data. Across all five sectors, that property does more work than any policy document.
Build those three, and the sector-specific work becomes configuration rather than re-architecture.
Next: Staffing an AI transformation · What DPDP 2027 means for your architecture